
Network Segmentation
Stop lateral movement before it reaches your controls. Segmentation gateways and access control keep IT incidents from spreading into OT systems — pre-tested in our lab, priced up front, ready to deploy.
- Pre-tested in our IT/OT lab
- Pricing published up front
- Spec’d, priced, shipped — no vendor onboarding
Shop Network Segmentation
3 lab-validated products
-
BlastShield Segmentation Gateway
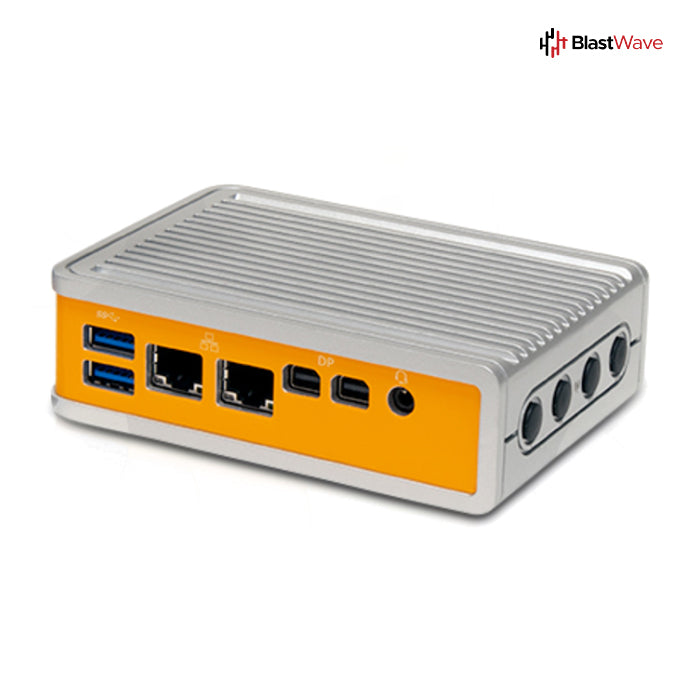 Vendor:BlastWave
BlastShield Segmentation Gateway
BlastShield simplifies the challenge of microsegmentation by creating simple peer-to-peer encrypted and authenticated...- Regular price
- From $2,180.00
- Sale price
- From $2,180.00
- Regular price
-
-
MOXA EDR-G9004-VPN-2MGTXSFTP-T Industrial Secure Router

SKU:EDR-G9004-VPN-2MGTXSFTP-T
Vendor:OT Cyber DirectMOXA EDR-G9004-VPN-2MGTXSFTP-T Industrial Secure Router
The EDR-G9004-VPN-2MGTXSFP-T is a four-port industrial secure router that puts firewall, NAT, VPN, and routing functi...- Regular price
- $2,300.00
- Sale price
- $2,300.00
- Regular price
-
-
OT Cybersecurity Starter Kit Bundle

SKU:OTCD-KIT-1
Vendor:OT Cyber DirectOT Cybersecurity Starter Kit Bundle
CyberScope XRF + BlastShield Segmentation Gateway Bundle Complete Edge Visibility + Zero-Trust Segmentation for Moder...- Regular price
- $14,500.00
- Sale price
- $14,500.00
- Regular price
-


Why segmentation is the first control that matters
Many organizations treat OT and IT networks separately due to the inherent differences in their security requirements. Segmentation and access control keep the two isolated so they interact only in a controlled manner — preventing threats from IT systems from spreading to OT systems.
Reduced attack surface
Keep adversaries from moving laterally across the network, and shrink the blast radius if a breach occurs.
Improved incident response
When an incident occurs, segmentation makes it faster to identify, isolate, and contain the affected segments.
Granular access control
Enforce strict policies on which users, devices, and systems can reach particular segments — protecting critical OT assets from accidental or malicious changes.
Regulatory compliance
IEC 62443, CMMC, NIST CSF and other frameworks put segmentation and access control at the top of their recommended controls.
Where segmentation sits in your architecture
Segmentation gateways create controlled boundaries between OT, IT, and cloud zones across sites — isolating control networks while orchestration stays centralized.
